Warning - you have received a subpoena email - blueAPACHE
Historical warning: 8 March 2016, concerning the fake AFP email campaign described below.
Further to our recent warning about fake Australia Post emails, a new ransomware email pretending to be from the Australian Federal Police (AFP) is now circulating.
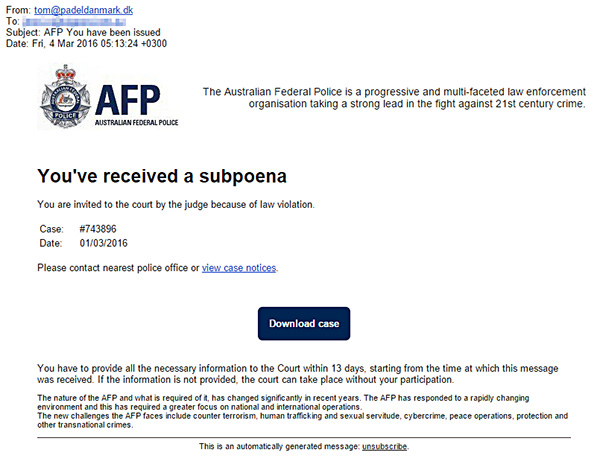
Branded with the AFP logo and the subject “AFP You have been issued”, the email claims you have been subpoenaed to appear in court due to a “law violation”. The email includes a case number and date. We have seen several of these over recent days. An example received is:
 The AFP have recently advised that they were aware of the fake email, and made a statement advising they do not issue subpoenas via email.
There were a few giveaway signs that this email was suspicious. The from address (tom@padeldanmark.dk) is from Denmark – not from the AFP, and the email includes an unsubscribe option, which seems strange considering this is supposedly a subpoena.
As always, when in doubt – phone the issuing body for clarification before clicking on links. If identified as fake or if you remain concerned, delete the email (and permanently delete the email from your deleted items folder or bin). Do not click on links contained in the email or reply to the email.
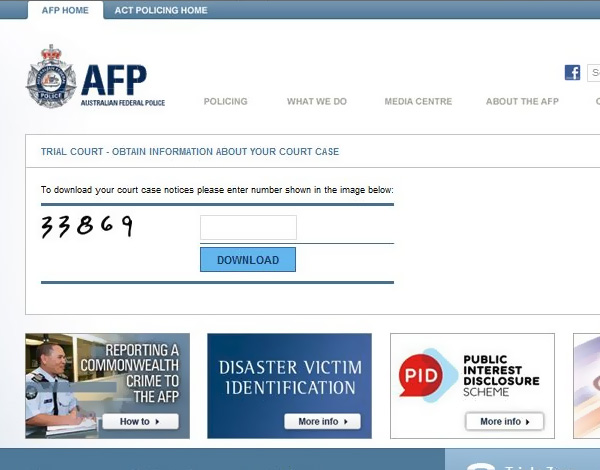
This latest ransomware email provides links (a text link and a button) that take you to a fake AFP website that requires completion of a captcha form to access your case details (see below). Completing the captcha form will result in downloading a zip file that appears to contain your court details, but is in fact the TorrentLocker ransomware.
 Once opened, TorrentLocker will usually attempt to delete volume shadow copies (to remove the chance of file recovery), copy itself to the windows directory and contact the command and control server. An encryption key is then generated and all accessible files on the network are encrypted. Upon encryption, the ransom message is displayed and details of the encrypted files are sent to the command and control server. TorrentLocker then harvests email accounts from your email programs (including online email accounts) and sends them to the command and control server to further spread the malware.
As with most ransomware, payment is made with bitcoins. TorrentLocker accepts a reduced fee if payment is made within a short period of time (usually four days), after which the price doubles. It is claimed that after one month the decryption key will be destroyed and encrypted files will be unrecoverable.
The decryption file is typically priced between $500 and $1000. Even when paying, there is no guarantee that you will receive the key to decrypt your files, or that the key will work.
If you have concerns about your security posture, would like staff security training, or would like to better understand how to protect your business, contact our account team.
Has the AFP confirmed whether it sends subpoenas via email?
Yes. The AFP advised that it was aware of the fake email and made a statement confirming that it does not issue subpoenas via email.
What were the warning signs that the AFP subpoena email was fake?
The email's "from" address (tom@padeldanmark.dk) originated from Denmark rather than the AFP, and the email included an unsubscribe option, which is unusual for a supposed legal subpoena.
What happens if you click the links in the fake AFP subpoena email?
The links (a text link and a button) take you to a fake AFP website requiring completion of a captcha form to access supposed case details. Completing the captcha results in downloading a zip file that appears to contain court details but actually contains the TorrentLocker ransomware.
What does the TorrentLocker ransomware do once it is opened?
TorrentLocker typically attempts to delete volume shadow copies to prevent file recovery, copies itself to the Windows directory, and contacts a command and control server. It then generates an encryption key, encrypts all accessible files on the network, displays a ransom message, and sends details of the encrypted files to the command and control server. It also harvests email accounts from email programs (including online accounts) and sends them to the command and control server to further spread the malware.
How is ransom typically paid for TorrentLocker, and what happens if payment is delayed?
Payment is made with bitcoins. TorrentLocker offers a reduced fee if payment is made within a short period (usually four days), after which the price doubles. It is claimed that after one month the decryption key is destroyed and encrypted files become unrecoverable.
How much does the TorrentLocker decryption typically cost, and is payment guaranteed to work?
The decryption file is typically priced between $500 and $1000. Even after paying, there is no guarantee of receiving a working decryption key.
What should you do if you receive a suspicious subpoena-style email?
According to us, you should phone the issuing body for clarification before clicking on any links. If the email is identified as fake or you remain concerned, delete it (and permanently delete it from your deleted items folder or bin), and do not click on links or reply to the email.
How does the article advise checking a suspicious subpoena-style email?
It advises phoning the purported issuing body to clarify the message before clicking links or replying. As a practical precaution, obtain the contact details independently from the body's official website rather than from the suspicious email.
What contractual notification duties may apply to a notice concerning Customer Data?
Check the actual notice and the agreement that applies to your service. Clause 14.2 of the published General Terms requires prompt notice to blueAPACHE and compliance with specified regulatory take-down, service-cessation and link-deletion notices or Telecommunications Industry Ombudsman directions relating to Customer Data. It does not state a universal immediate-notification duty for every subpoena or legal demand.
Who can businesses contact for help with security concerns or staff security training related to this type of threat?
Businesses with concerns about their security posture, who want staff security training, or who want to better understand how to protect their business can contact our account team.
When was your warning about the fake AFP subpoena email published?
The article was published on March 8, 2016, and is written by us.
Images on This Page
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a6ffec7d87be5a881637bba_31b5a84971e1d1ce71dc99ca059bfbde_blueAPACHE.svg
blueAPACHE logo on a dark blue background
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701c03b153d68a8eeb8f4a_Ransomware-Warning.avif
(no alt text)
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a713402a5a7f7ebf553f0bf_Background-Top.avif
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701c06b153d68a8eeb9024_afp.jpeg
AFP Ransomware Email
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701c06b153d68a8eeb9021_afp-captcha.jpeg
AFP Catcha Form
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701b59b153d68a8eeb0e36_BBanner-1-Windows-10-is-out.-AI-is-in.-.avif
You’ve Invest in Security. So Why Are Breaches Still Happening?
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bb807b7741bf53e298a_BBanner-1-Windows-10-is-out.-AI-is-in.-8.avif
EOFY 2026: The Reset Is Done – Now It’s About Getting Ahead
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbb07b7741bf53e29d0_BBanner-2-When-support-ends-risk-begins-4.avif
Why Every Business Needs AI Guardrails
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbb07b7741bf53e29d7_BBanner-2-When-support-ends-risk-begins-3.avif
Ransomware Incident Response: Why Paying the Ransom Is a Failure of Preparation
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bb707b7741bf53e297d_BBanner-2-When-support-ends-risk-begins-1.avif
The 7 Cyber Truths Boards Must Act On In 2026
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e29f9_BBanner-1-Windows-10-is-out.-AI-is-in.-7.avif
Reflecting on an Outstanding 2025 – Thank You for Your Partnership
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e2a0c_Procurement-Portal.avif
The blueAPACHE e-Store: IT purchasing made simple
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e29ec_BBanner-1-Windows-10-is-out.-AI-is-in.-5.avif
Building Our Cyber Safe Culture: A Practical Guide for CSAM 2025
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fbfad31fa678fefd51a_6a704f395a0a01b8e482853a_support-monitor.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc4563e_6a704f3a400fc8e661400519_support-user.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45639_6a704f3a91ffd7d0dbc40847_support-phone.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc4562f_6a704f3747d60bd3f65b7a31_support-globe.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45636_6a704f38eb60992797acf5d9_support-mail.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45633_6a704f3a07b7741bf54f2122_support-speech-bubble.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a707520ca872d1b5a69a518_Sensiba.avif
Sensiba ISO/IEC 27001 Certified badge with a diamond-shaped logo below the text.