Concerns for Cloud security? Best look internally - blueAPACHE
2015
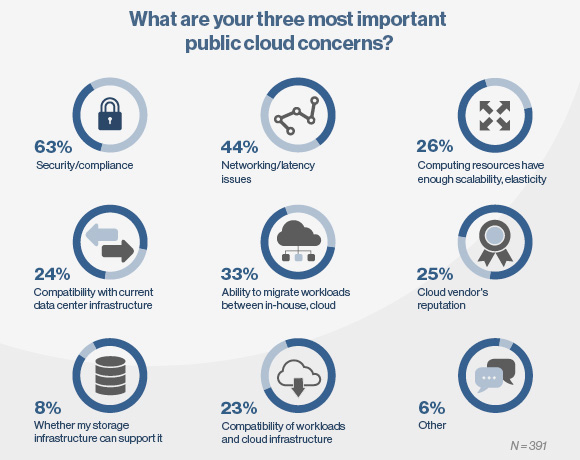
Sixty-three percent of IT professionals cite security as a top concern with public cloud according to Tech Buyer Snapshot. A separate survey of 300 IT security professionals conducted last year showed the percentage of respondents who preferred to keep sensitive corporate data on-premises rather than in the cloud was eighty percent.
While perceptions of cloud security may be improving, the real threat to cloud security may not have anything to do with the service provider.
 At the recent Gartner Symposium/ITxpo 2016 in Orlando, Daryl Plummer presented on humanity and technology. He stated that through 2020, 95 percent of cloud security failures will be the customer’s fault.
While organisations still harbour security concerns about the use of public cloud services, only a small percentage of security incidents impacting enterprises using the cloud have been due to vulnerabilities that were the provider’s fault.
Cloud providers invest heavily in security, prevention and recovery. Their business relies on it. More often than not, customers will look to blame their service provider for breaches and data loss before assessing internal policies, procedures and security – despite studies showing that the leading cause of data loss is human error. Plummer believes this will lead to customers seeking cloud access security brokers products to manage and monitor their use of SaaS and other forms of public cloud services.
Security is key to successfully leveraging the many benefits of the cloud, especially with the lack of clarity on data sovereignty, new data retention laws and recent changes to the Privacy Act. Despite the suggestion that security issues will likely be caused by in-house issues, we strongly encourage organisations to perform due diligence on their cloud providers to ensure they meet the changing compliance and regulatory requirements faced in Australia.
To better understand cloud security (and the processes you can put in place to better secure your cloud connectivity), contact the blueAPACHE Cloud team.
What percentage of IT professionals cite security as a top concern with public cloud, according to the blueAPACHE article?
According to the Tech Buyer Snapshot survey cited in our article, sixty-three percent of IT professionals cite security as a top concern with public cloud.
According to Gartner's Daryl Plummer, what proportion of cloud security failures will be the customer's fault through 2020?
At the Gartner Symposium/ITxpo 2016 in Orlando, Daryl Plummer stated that through 2020, 95 percent of cloud security failures will be the customer's fault.
What do customers tend to do when breaches or data loss occur, ?
customers will more often than not look to blame their service provider for breaches and data loss before assessing their own internal policies, procedures and security.
What is cited as the leading cause of data loss ?
studies show human error is the leading cause of data loss.
What solution does Daryl Plummer believe customers will seek in response to cloud security concerns?
Plummer believes customers will seek cloud access security broker products to manage and monitor their use of SaaS and other forms of public cloud services.
Why do you still recommend organisations perform due diligence on their cloud providers despite the customer-fault trend?
Despite the suggestion that security issues will likely be caused by in-house issues, blueAPACHE strongly encourages organisations to perform due diligence on their cloud providers to ensure they meet the changing compliance and regulatory requirements faced in Australia, given the lack of clarity on data sovereignty, new data retention laws, and recent changes to the Privacy Act.
Who should be contacted for help understanding cloud security according to the blueAPACHE article?
We advise contacting our Cloud team to better understand cloud security and the processes that can be put in place to better secure cloud connectivity.
Images on This Page
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a6ffec7d87be5a881637bba_31b5a84971e1d1ce71dc99ca059bfbde_blueAPACHE.svg
blueAPACHE logo on a dark blue background
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701c0fddcde676dc9f31ef_cloud-security.avif
(no alt text)
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a713402a5a7f7ebf553f0bf_Background-Top.avif
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701c13ddcde676dc9f3296_Cloud-security-concern.jpeg
Cloud security concerns report
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701b59b153d68a8eeb0e36_BBanner-1-Windows-10-is-out.-AI-is-in.-.avif
You’ve Invest in Security. So Why Are Breaches Still Happening?
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bb807b7741bf53e298a_BBanner-1-Windows-10-is-out.-AI-is-in.-8.avif
EOFY 2026: The Reset Is Done – Now It’s About Getting Ahead
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbb07b7741bf53e29d0_BBanner-2-When-support-ends-risk-begins-4.avif
Why Every Business Needs AI Guardrails
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbb07b7741bf53e29d7_BBanner-2-When-support-ends-risk-begins-3.avif
Ransomware Incident Response: Why Paying the Ransom Is a Failure of Preparation
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bb707b7741bf53e297d_BBanner-2-When-support-ends-risk-begins-1.avif
The 7 Cyber Truths Boards Must Act On In 2026
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e29f9_BBanner-1-Windows-10-is-out.-AI-is-in.-7.avif
Reflecting on an Outstanding 2025 – Thank You for Your Partnership
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e2a0c_Procurement-Portal.avif
The blueAPACHE e-Store: IT purchasing made simple
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a701bbc07b7741bf53e29ec_BBanner-1-Windows-10-is-out.-AI-is-in.-5.avif
Building Our Cyber Safe Culture: A Practical Guide for CSAM 2025
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fbfad31fa678fefd51a_6a704f395a0a01b8e482853a_support-monitor.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc4563e_6a704f3a400fc8e661400519_support-user.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45639_6a704f3a91ffd7d0dbc40847_support-phone.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc4562f_6a704f3747d60bd3f65b7a31_support-globe.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45636_6a704f38eb60992797acf5d9_support-mail.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a70181278f802e23979d547/6a704fd991ffd7d0dbc45633_6a704f3a07b7741bf54f2122_support-speech-bubble.svg
(no alt text)
-
https://cdn.prod.website-files.com/6a6ffec7d87be5a881637bb3/6a707520ca872d1b5a69a518_Sensiba.avif
Sensiba ISO/IEC 27001 Certified badge with a diamond-shaped logo below the text.